Findings Management
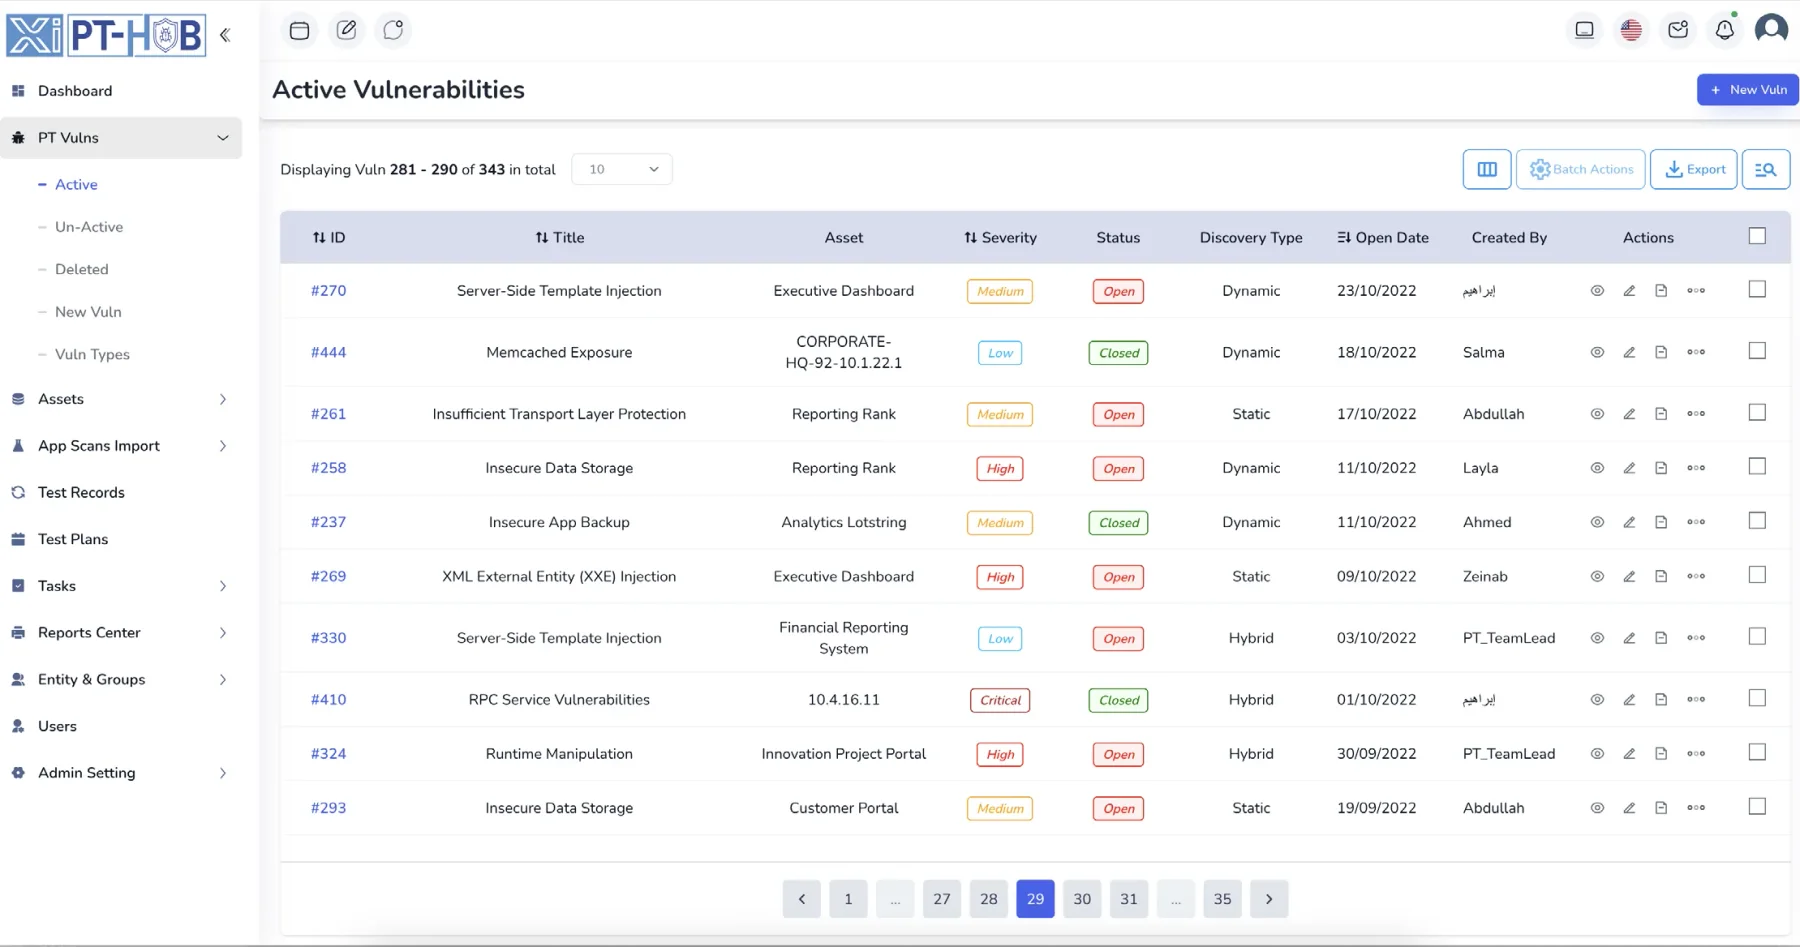
Track and manage every vulnerability discovered during testing, from first report to verified fix.
Key Capabilities: Severity classification | Evidence | Retest status | Audit trail
PT-Radar gives security teams one place to scope assets, execute tests, document findings and prove remediation, with a full audit trail behind every step.
deployment, to fit your policy
data hosting, inside the Kingdom
box methodologies supported
behind every finding and change
PT-Radar replaces all of it with one system built for how penetration tests actually run.
Scope lives in a spreadsheet, findings in a scanner export, evidence on a shared drive and status in email. Nothing reconciles.
Every report gets rebuilt by hand. Proving the work takes as long as doing it.
When an auditor asks who changed a finding and when, the answer is a search through chat history.
Raised by the GrayBox test TC-42, evidence attached, assigned to the asset owner.
The fix was verified by a retest; the full history stays in the audit trail.
Track and manage every vulnerability discovered during testing, from first report to verified fix.
Key Capabilities: Severity classification | Evidence | Retest status | Audit trail
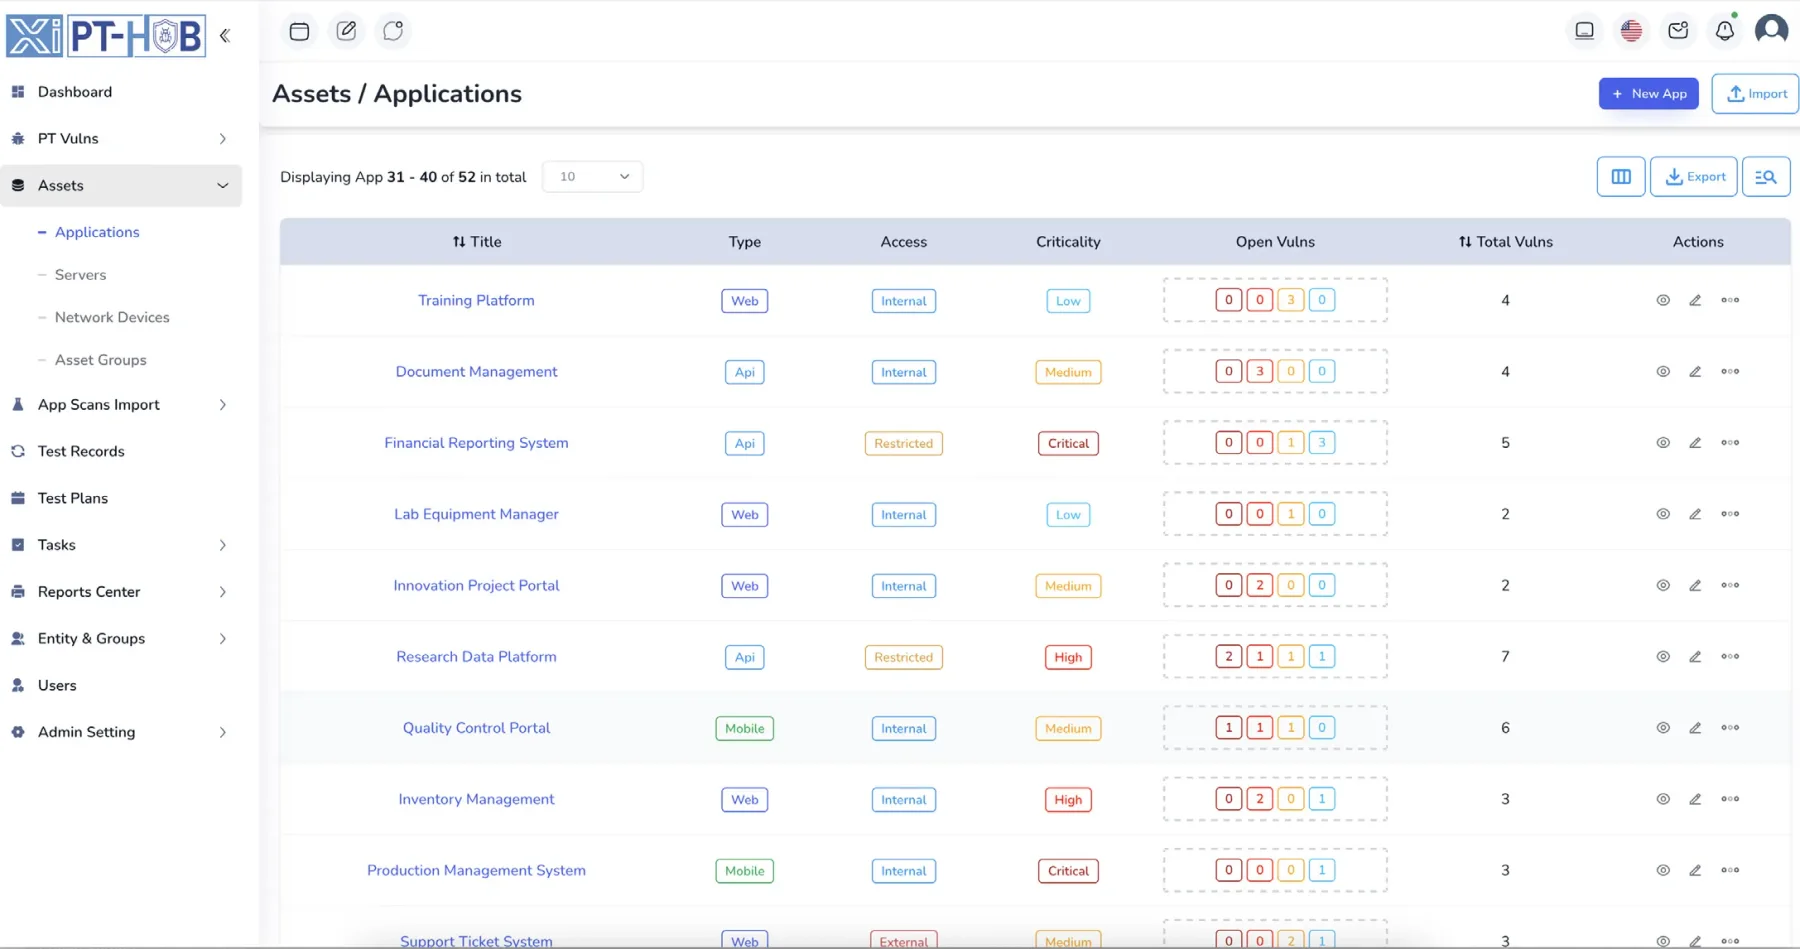
A central inventory of applications, servers and network devices, grouped the way your organization works.
Key Capabilities: Applications | Servers | Network devices | Entity groups
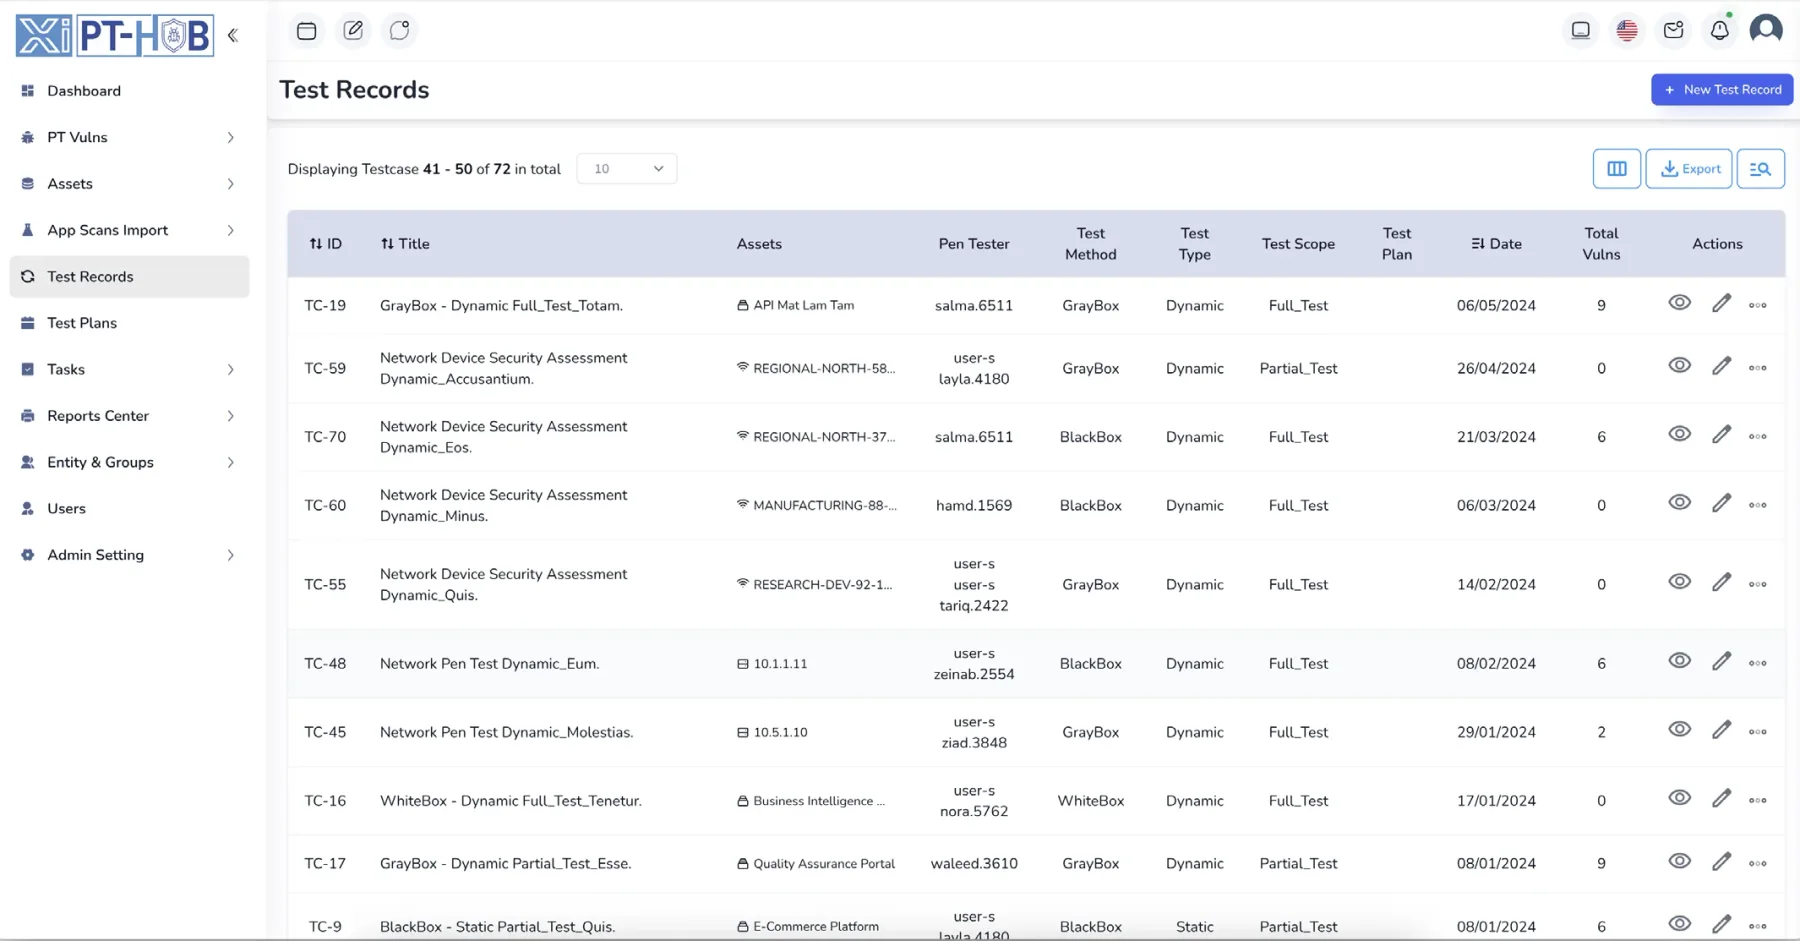
Plan tests by methodology, assign testers and follow progress in real time.
Key Capabilities: BlackBox | GrayBox | WhiteBox | Task assignment
Reports for technical, management and compliance readers, backed by a full activity log.
Key Capabilities: Custom templates | Executive dashboards | Activity monitoring
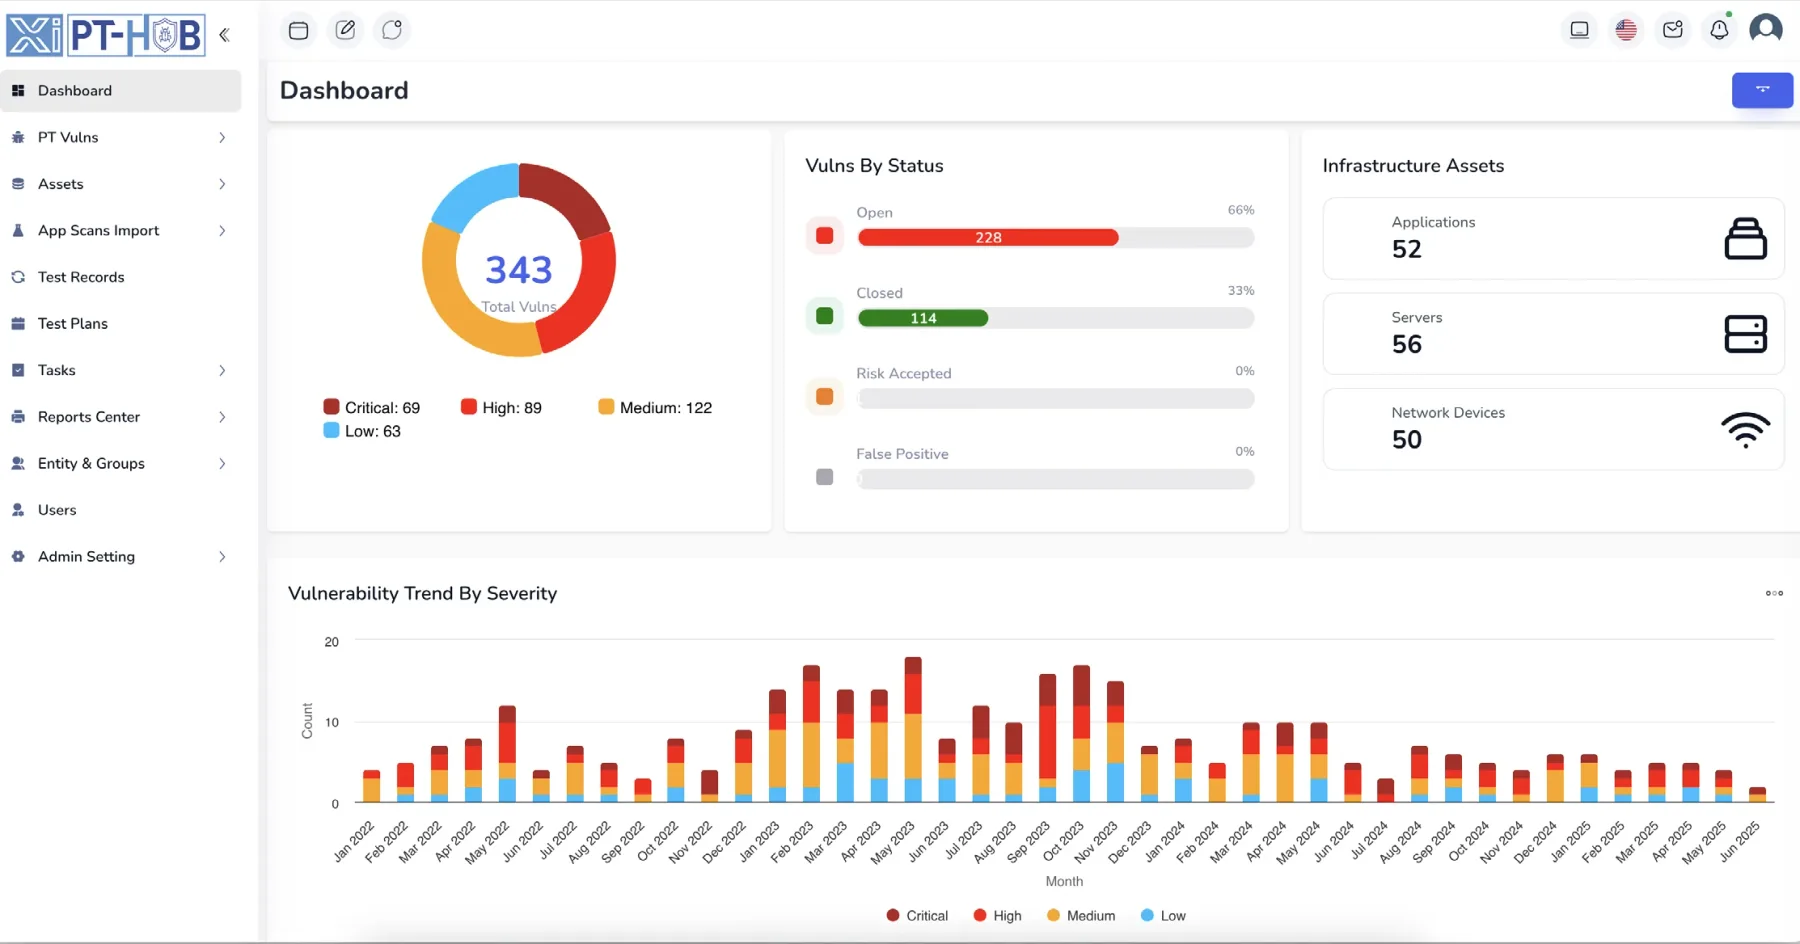
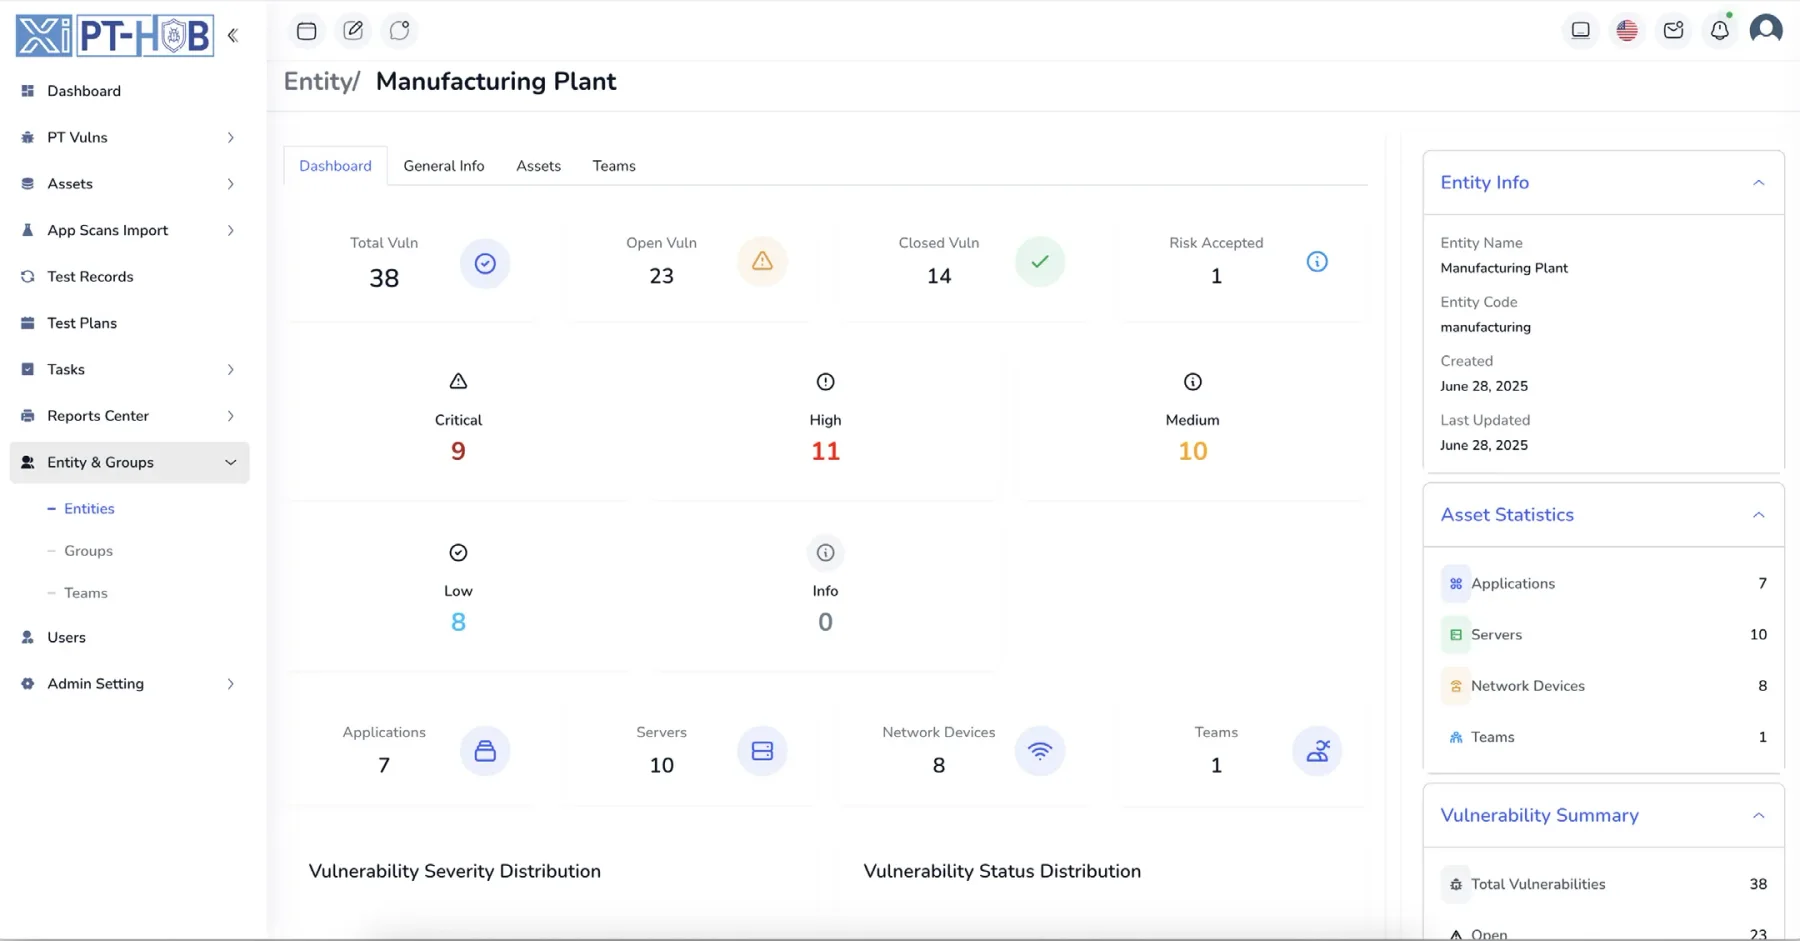
Three views your teams use every day. Hover over a screen to magnify it, and select a numbered point to see what that part does.
Screens shown with sample data.
The teams that run offensive security.
Track and manage vulnerabilities discovered during testing with structured categorization, risk assessment and detailed reporting.
A real-time security overview with customizable widgets, vulnerability statistics, risk metrics and executive-level reporting.
Complete entity isolation, customizable entity groups and granular user access control for secure organizational separation.
Role-based access control, team management and collaborative workflows built for penetration testing teams.
A comprehensive asset inventory covering applications, servers and network devices with detailed tracking and organization.
Generate detailed security reports, risk assessments and compliance documentation using customizable templates.
Structured test planning and case management with progress tracking and task assignment.
A comprehensive audit trail with real-time activity tracking, user behavior monitoring and detailed system event logging.
Seamless integration with popular security scanners and tools for consolidated vulnerability management.
Cloud or on-premise
The same vulnerability, tracked through every stage of the lifecycle: scoped, tested, reported and retested.
Public and private sector security functions running their own testing programs.
MSSPs coordinating testing across many client environments at once.
Independent practitioners who need structure without enterprise overhead.
Consultancies delivering assessments under their own methodology and brand.
GRC departments who need evidence, not screenshots pasted into a document.
Auditors who need to see what changed, who changed it and when.
Security you can show an auditor.
Test plans can be created using BlackBox, GrayBox or WhiteBox methodology, and the platform supports both structured and ad hoc penetration testing approaches.
Yes. PT-Radar integrates with popular security scanners so imported results and manually documented findings live together in one vulnerability list.
Yes. The multi-tenant architecture provides complete entity isolation, customizable entity groups and granular user access control.
Role-based access control gives fine-grained permissions per user, which is what lets you safely involve internal staff, external testers and clients in the same project.
Reports can be generated for different readers (technical teams, management and compliance) in multiple formats, using customizable templates.
A full audit trail and evidence repository sit behind every project, with real-time activity tracking and detailed system event logging for compliance and security oversight.
Yes. PT-Radar is available both as a cloud deployment and on-premise, so it can run inside your own environment where policy requires it.
Data is hosted within Saudi Arabia.
Pricing is quoted per deployment. Tell us your team size and what you need to cover, and we will send a quotation.
Support is available during business hours.
Request a demo and we will walk through the workflow with your assets, your methodology and your reporting requirements.