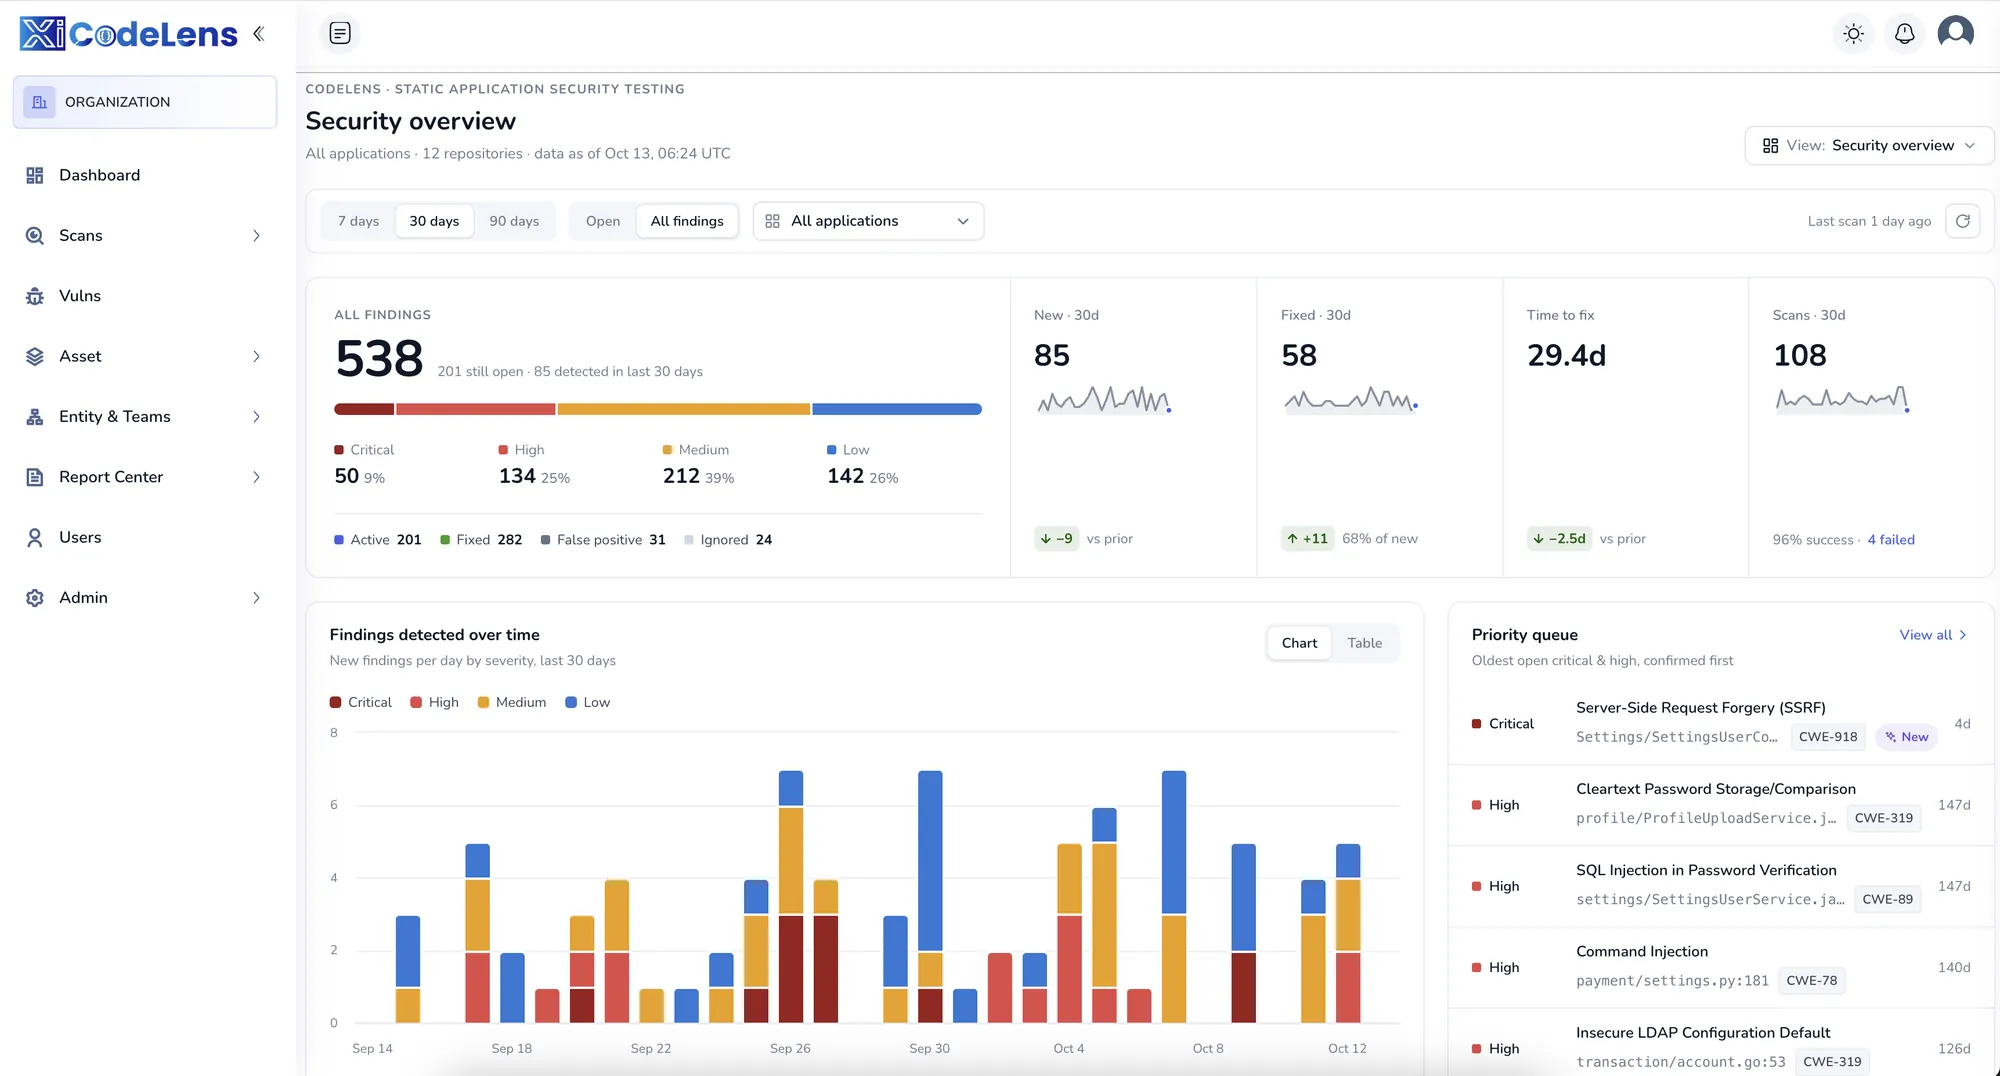
Vulnerability Management
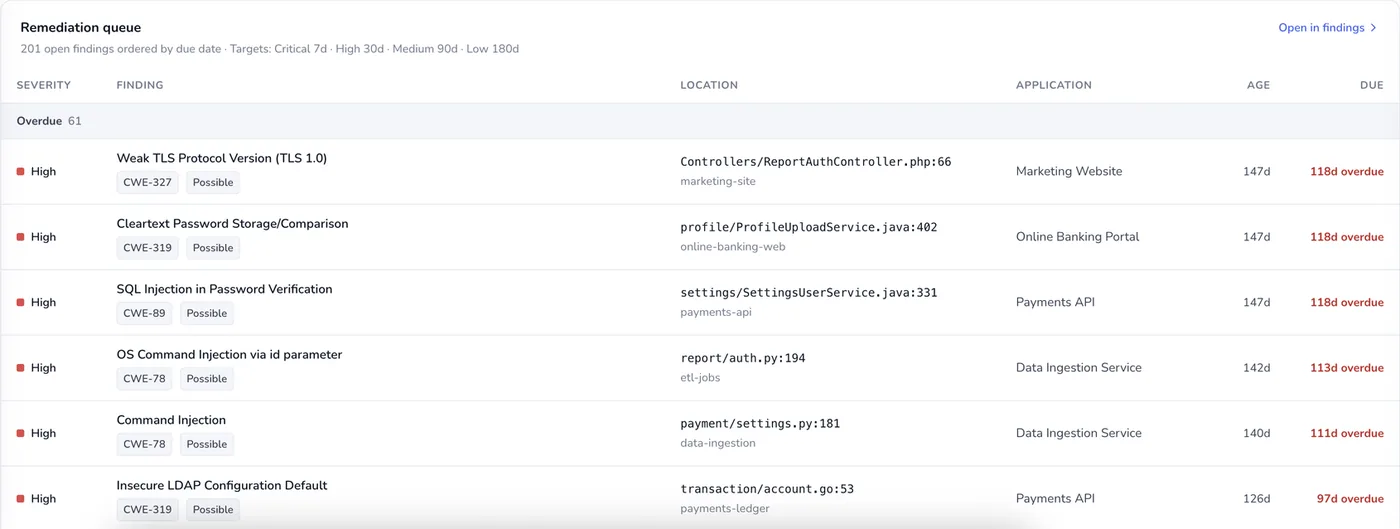
A comprehensive dashboard to track, prioritize and remediate security vulnerabilities.
Key Capabilities: Severity triage | Validation status | Due-date tracking | CWE tagging
CodeLens is an advanced Static Application Security Testing (SAST) tool that leverages the power of artificial intelligence to help developers and security teams identify and mitigate security vulnerabilities in source code more effectively.
fewer false positives, thanks to contextual understanding
languages supported, with their leading frameworks
categories that every finding is mapped to
applications tracked in one central inventory
CodeLens combines trained detection models with an understanding of how your application works, so developers spend their time on the vulnerabilities that matter.
Pre-trained models detect vulnerabilities with near-zero false positives.
Understands your application's business logic and architecture to reduce false positives by up to 95%, delivering only relevant security insights.
boolean verifyPassword(String user, String password) {
    String q = "SELECT * FROM audit WHERE tag='" + TAG + "'";
    jdbc.execute(q);

    String sql = "SELECT id FROM users WHERE name='" + user
        + "' AND password='" + password + "'";
    return !jdbc.queryForList(sql).isEmpty();
}
Confirmed: the user-supplied password reaches the query without sanitization.
TAG is a build-time constant, so there is no input an attacker can inject.
A comprehensive dashboard to track, prioritize and remediate security vulnerabilities.
Key Capabilities: Severity triage | Validation status | Due-date tracking | CWE tagging
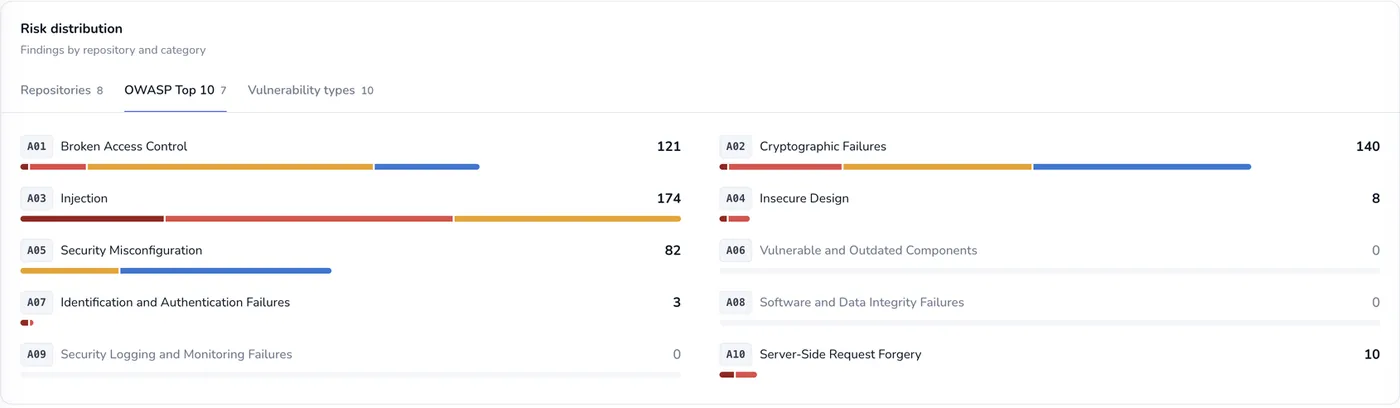
A centralized inventory of your web, mobile and API applications.
Key Capabilities: Web apps | Mobile apps | APIs | Risk by repository
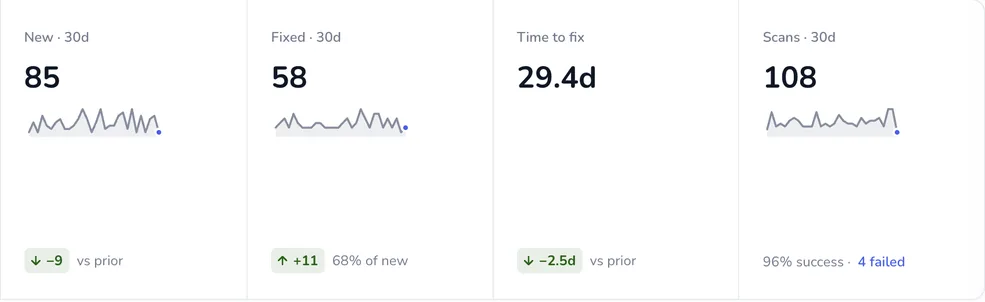
Assess the security posture and productivity of your development teams.
Key Capabilities: Time to fix | Fix rate | Backlog age
Automated generation and distribution of customized reports, for efficient tracking and analysis of key metrics across the organization.
Key Capabilities: Custom reports | Automated distribution | Organization-wide metrics
Three views your teams use every day. Hover over a screen to magnify it, and select a numbered point to see what that part does.
Screens shown with sample data.
CodeLens scans the languages enterprise teams build with, including their most popular frameworks.
Spring · Jakarta EE
Django · Flask
Node.js · React · Angular
Ask us about your stack
Give leadership, security and development teams the same up-to-date picture of your application security.
Talk to the CyberX team about a CodeLens demo and how it fits your applications and workflow.